Direct Drive Reads: A Double-Edged Technique in Cybersecurity
In cybersecurity, Direct Drive Reads (DDR) refer to accessing raw disk sectors directly—bypassing the filesystem and operating system APIs. This technique allows security researchers, forensic analysts, and adversaries alike to interact with the disk at a low level. It can be used for legitimate forensic investigations or stealthy malicious activities.
This article explains what Direct Drive Reads are, their significance, and how they are leveraged by both Red Teams (attackers/penetration testers) and Blue Teams (defenders/forensic analysts).
What Are Direct Drive Reads?
Normally, applications interact with files through the operating system's filesystem (e.g., NTFS, ext4, FAT32). However, a Direct Drive Read bypasses this abstraction and interacts with the raw disk device.
On Windows, this typically means opening a device handle such as \\.\PhysicalDrive0.
On Linux, it may involve reading from /dev/sda or /dev/nvme0n1.
This gives full access to the disk's bytes, regardless of filesystem structures, permissions, or OS-level controls.
Why Use Direct Drive Reads?
Forensics & Recovery
Investigators can carve deleted files from unallocated space.
Analysts can examine hidden partitions, slack space, or remnants of wiped data.
Malware & Evasion
Attackers can bypass operating system APIs to hide their tracks.
Rootkits may read/write sectors directly to manipulate boot records or implant persistence.
Data Extraction
Red Teams may use DDR to extract sensitive information from areas not normally accessible via APIs.
Blue Teams may use DDR to verify integrity of disk images against tampering.
Code Examples
Warning Running these examples requires administrative/root privileges. Misuse can damage the disk.
This produces a complete sector-by-sector image, ensuring hidden or deleted data is preserved.
Defensive Strategies Against Malicious DDR
Endpoint Detection & Response (EDR): Monitor raw disk access attempts.
Least Privilege: Prevent unprivileged users from accessing physical drives.
Firmware Integrity Checks: Verify boot sector and firmware against trusted baselines.
Logging & Alerting: Unusual attempts to open \\.\PhysicalDrive0 or /dev/sdX should trigger alerts.
Conclusion
Direct Drive Reads represent a powerful but double-edged technique. For defenders, they are essential for forensic accuracy and incident response. For attackers, they provide a stealthy path to data exfiltration, persistence, and evasion.
Both Red and Blue teams must understand DDR deeply: attackers to exploit it, defenders to detect and prevent its abuse. Ultimately, awareness and monitoring are key to keeping this powerful capability under control.
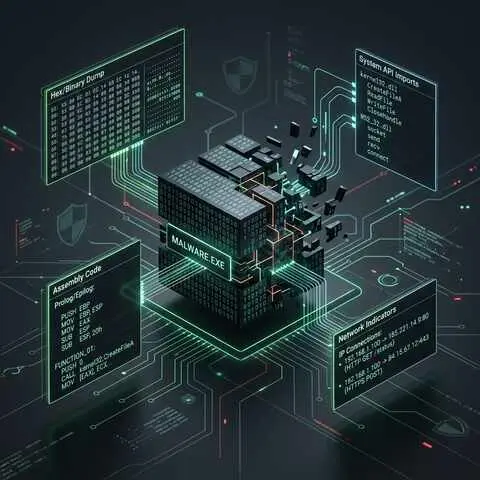
 Malware Analysis