The Legacy of Stuxnet: How a Worm Changed the Landscape of Geopolitical Cyber Warfare
A technical and strategic analysis of Stuxnet, examining zero-day weaponization, PLC rootkits, air-gap subversion, and modern ICS/SCADA defense architectures.
Explore the world of cybersecurity with in-depth articles and guides. From ethical hacking to threat defense, master the skills to protect digital assets.
A technical and strategic analysis of Stuxnet, examining zero-day weaponization, PLC rootkits, air-gap subversion, and modern ICS/SCADA defense architectures.
A comprehensive deep dive into boot sector viruses and modern bootkits, exploring pre-OS execution mechanics, hidden forensic complications, Infrastructure as Code (IaC) golden image risks, and enterprise-grade protection architectures.
A comprehensive deep dive into how rigorous change management protects systems throughout every phase of the software update lifecycle, from vulnerability triage to progressive deployment and automated rollback.
An in-depth guide to bare metal (Type 1) virtualization, exploring how it works, real-world implementations, and the unique security challenges it presents for Blue Teams.
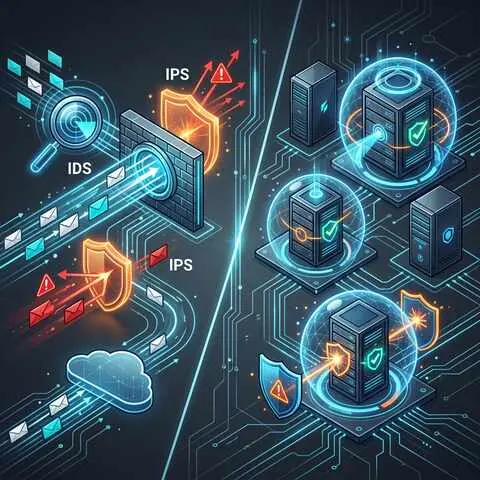
A deep dive into the world of intrusion detection and prevention systems. Understand the critical differences, functionalities, and use cases of IDS, IPS, HIDS, and HIPS in modern cybersecurity.
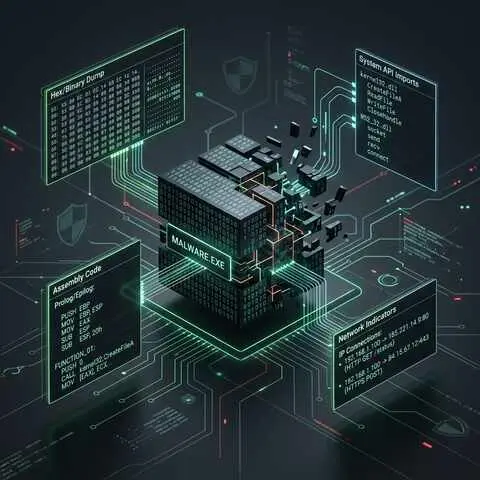
A comprehensive, technical exploration of malware decomposition, guiding security analysts through static, dynamic, memory, and code analysis phases to dissect complex binaries.
A comprehensive deep dive into the STRIDE threat modeling framework, exploring Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege, complete with mitigation strategies and practical implementation techniques.
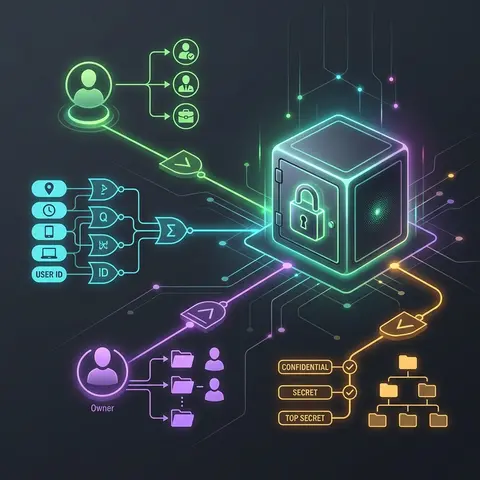
An in-depth analysis of Discretionary, Mandatory, Role-Based, and Attribute-Based Access Control models, their pros and cons, and real-world deployment scenarios.
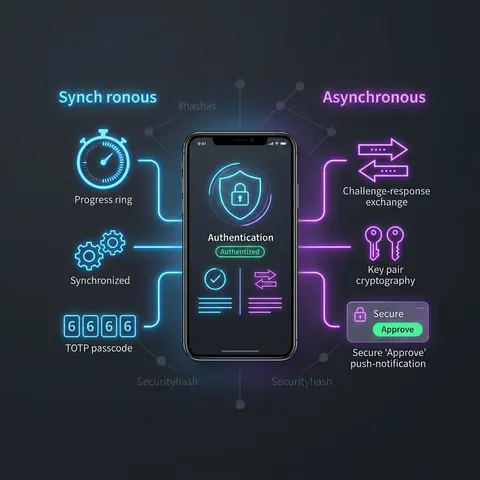
Learn how software tokens work in modern authentication systems, the differences between synchronous and asynchronous token mechanisms, real-world use cases, security considerations, and implementation best practices.
A comprehensive technical breakdown of SAML, OAuth 2.0, and OpenID Connect (OIDC), explaining their core mechanics, how they differ, and how they interoperate in modern identity architectures.