Intrusion Prevention with Fail2Ban: Architecture, Jail Configuration, and Enterprise Hardening
Every internet-facing service operates under constant hostile reconnaissance.
Automated botnets, script kiddies, and distributed adversary infrastructure continuously cycle through IPv4 and IPv6 subnets, probing for open ports and vulnerable application endpoints.
According to threat intelligence telemetry, an unhardened server with an exposed SSH daemon on TCP port 22 receives thousands of unauthorized authentication attempts every single hour.
Adversaries leverage automated credential stuffing, dictionary attacks, and exploit payloads mapped directly to MITRE ATT&CK techniques T1110 (Brute Force), T1595 (Active Scanning), and T1190 (Exploit Public-Facing Application).
While perimeter defenses like cloud Web Application Firewalls (WAFs) and border gateways filter Layer-7 web traffic, host-level endpoints remain uniquely vulnerable to direct IP access, unauthorized lateral movement, and brute-force exhaustion.
Relying solely on passive log collection leaves organizations exposed to rapid credential guessing before Security Operations Center (SOC) analysts can triage alerts.
Conversely, static IP whitelisting is often operationally impractical for public-facing web applications, mail transfer agents, and distributed developer workforces.
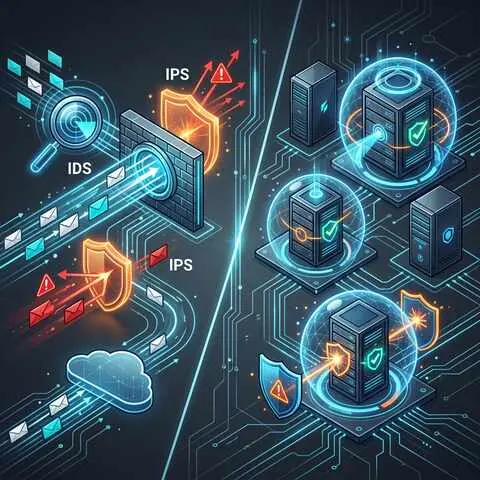
Fail2Ban bridges this critical operational gap as a battle-tested, lightweight host-based intrusion prevention system (HIPS).
Written in Python and natively integrated with the Linux netfilter subsystem, Fail2Ban continuously inspects real-time system logs, identifies malicious behavior through deterministic regular expressions, and injects dynamic packet-filtering rules into the kernel firewall.
This guide delivers an architectural breakdown, enterprise jail configurations, custom regex filter engineering, nftables/ipset performance optimizations, and compliance governance for production deployments.
1. Fail2Ban Architecture and Netfilter Mechanics
To engineer robust defenses, engineers must understand how Fail2Ban interacts with both userspace logging daemons and kernel-space packet routing.
Fail2Ban is architected around a client-server model consisting of fail2ban-server (the multi-threaded background daemon) and fail2ban-client (the administration and control interface).
Fail2Ban structures its defensive workflows across four discrete operational abstractions:
Filters (/etc/fail2ban/filter.d/):
Pattern definitions specifying regular expressions (failregex) that match suspicious log entries.
Filters capture the attacking IP address using the standardized <HOST> regex macro.
They also define ignoreregex strings to filter out benign anomalies and prevent false positives.
Actions (/etc/fail2ban/action.d/):
Script templates defining the exact operating system commands executed when an IP triggers or clears a ban.
Actions typically manipulate packet filters (nftables, iptables, firewalld), update access control lists, generate syslog notifications, or dispatch webhooks to incident management systems.
Jails (/etc/fail2ban/jail.d/):
The unifying operational entity that binds a specific filter to one or more actions and associates them with a log target.
A jail specifies the threshold logic: how many failed attempts (maxretry) within a rolling detection window (findtime) warrant a temporary or permanent block (bantime).
Persistent Database (/var/lib/fail2ban/fail2ban.sqlite3):
An embedded SQLite database that tracks historic failures, active bans, and ticket lifetimes.
This persistence ensures that restarting the server or cycling the daemon does not drop active security bans, mitigating reboot-evasion tactics.
Log Monitoring Backend Comparison
Fail2Ban supports several backends to monitor log file alterations.
Choosing the correct backend directly impacts system CPU utilization and detection latency:
Backend
Mechanism
Kernel Resource Overhead
Latency
Best Suited For
systemd
Direct API query into the journald binary log ring
Low
Sub-second
Modern Linux distributions utilizing systemd exclusively
pyinotify
Linux inotify kernel file-change events
Very Low
Real-time
High-throughput flat log files (/var/log/*.log)
polling
Periodic stat() polling on target file descriptors
Moderate to High
High (1-second intervals)
Network mounts (NFS/CIFS) or environments where inotify is unavailable
gamin
Gamin file alteration monitor library
Moderate
Near real-time
Legacy systems requiring abstract file watching
For modern enterprise infrastructure (Ubuntu 22.04/24.04, Debian 12, RHEL 9), configuring backend = systemd is strongly recommended for system services.
For standalone container logs or dedicated web access logs, pyinotify offers peak efficiency.
2. Enterprise Configuration Architecture: Jails and Defaults
A frequent failure mode in Fail2Ban deployments is editing upstream package configuration files directly.
When system packages update, upstream package managers overwrite /etc/fail2ban/jail.conf and /etc/fail2ban/fail2ban.conf, silently stripping custom defenses.
The Hierarchical Override Pattern
Fail2Ban processes configuration files in strict alphabetical and extension order.
Local configuration files (.local) override default configuration files (.conf), and modular files in .d/ directories take highest precedence:
/etc/fail2ban/fail2ban.conf (Upstream defaults - do not touch)
/etc/fail2ban/jail.d/*.local (Individual service jail specifications)
Step 1: Establishing Hardened Global Defaults (jail.local)
Create /etc/fail2ban/jail.local to define global thresholds, baseline whitelists, and packet-filtering actions:
[DEFAULT]# Whitelist trusted infrastructure: loopback, local subnets, VPN gateways, jump hostsignoreip = 127.0.0.1/8 ::1 10.0.0.0/8 192.168.1.0/24 203.0.113.50# Detection window: count failures occurring within the last 15 minutesfindtime = 15m# Threshold: trigger ban after 4 failed attempts within findtimemaxretry = 4# Ban duration: initial penalty of 2 hoursbantime = 2h# Use progressive/exponential ban duration scalingbantime.increment = truebantime.rndtime = 15mbantime.maxtime = 60dbantime.factor = 2# Monitoring backend (systemd journald integration)backend = systemd# Firewall action: modern nftables multiport filteringbanaction = nftables-multiportbanaction_allports = nftables-allports# Notification settingsmta = maildestemail = soc-alerts@example.comsender = fail2ban@internal.example.comaction = %(action_mwl)s
Explaining Exponential Ban Increments
Static ban times create a predictable cost model for attackers.
A botnet script can deliberately pause for bantime + 1 seconds before resuming credential spraying.
Enabling bantime.increment = true shifts the asymmetry back to defense.
When an attacker repeatedly triggers bans, Fail2Ban calculates subsequent ban intervals using an exponential formula:
With bantime.rndtime enabled, Fail2Ban injects randomized jitter into the unban timestamp.
This prevents botnets from synchronizing retry attacks across coordinated bot swarms.
3. Production Service Jails: SSH, Nginx, and Recidive
Enterprise servers require defense against specific protocols and behavioral patterns.
Below are production-ready jail configurations deployed in /etc/fail2ban/jail.d/.
Setting mode = aggressive instructs the SSH filter to flag not only invalid passwords, but also unauthorized user enumeration, pre-authentication timeouts, and reverse DNS mapping failures.
2. Nginx Web Protection Jails (/etc/fail2ban/jail.d/nginx.local)
Web servers face aggressive vulnerability scanners scanning for unpatched WordPress plugins, exposed .env credentials, and API weaknesses.
3. The Recidive Jail: Locking Out Chronic Offenders (/etc/fail2ban/jail.d/recidive.local)
The recidive jail is Fail2Ban's most potent weapon against persistent threat actors.
It monitors Fail2Ban's own operational log (/var/log/fail2ban.log).
If an IP address is banned repeatedly across any other jail within a 24-hour cycle, the recidive jail escalates the punishment to an aggressive, multi-week quarantine across all ports.
+----------------------------------------------------------------------------------------------------+| RECIDIVE ESCALATION WORKFLOW || || Adversary IP: 198.51.100.45 || │ || ├──> Probes Port 22 (SSH) ───> sshd jail triggers ───> Banned for 24 hours || ├──> Unbanned after 24 hrs || ├──> Probes Port 443 (.env) ───> nginx-botsearch triggers ───> Banned for 48 hours || ├──> Unbanned after 48 hrs || └──> Probes Port 80 (404s) ───> nginx-notfound triggers ───> Third ban event || │ || ┌──────────────────────────────────────────────────────────────────────┘ || ▼ || Recidive Jail detects 3 bans in /var/log/fail2ban.log within 24 hours || ===> ACTION: Total firewall quarantine across ALL TCP/UDP ports for 30 DAYS |+----------------------------------------------------------------------------------------------------+
4. Custom Filter Engineering and Regex Optimization
Pre-packaged filters cover standard applications, but proprietary APIs, internal authentication portals, and microservice micro-gateways require custom filter rules.
Anatomical Rules for Custom Failregexes
A valid Fail2Ban filter must adhere to four strict principles:
IP Anchoring:
Every regex must capture the attacking network address using the special <HOST> token.
Behind the scenes, Fail2Ban expands <HOST> into an optimized regex matching both IPv4 and IPv6 addresses.
Deterministic Matching:
Avoid unbounded wildcards like .*.
Greedy quantifiers introduce catastrophic regex backtracking, which adversaries can exploit to cause Denial of Service against the logging daemon.
Prefix Decoupling:
Modern filters utilize the prefregex directive to match common syslog or journal headers once, avoiding repetitive processing across multiple failregex branches.
Date Isolation:
Do not attempt to parse timestamps in the failregex.
Fail2Ban handles date stripping in an isolated preprocessing stage.
Building a Custom Nginx Filter for Sensitive File Probing
Suppose adversaries are fuzzing your web cluster for exposed secrets (.env, .git/config, wp-config.php, backup.sql).
Create /etc/fail2ban/filter.d/nginx-botsearch.local:
[Definition]# Match standard Nginx combined log formatting:# IP - - [Date] "METHOD /path HTTP/X" STATUS BYTES "REFERER" "USER-AGENT"failregex = ^<HOST> - \S+ \[\] "(GET|POST|HEAD) \/(?:\.env|\.git|\.aws|\.docker|wp-login\.php|xmlrpc\.php|config\.json|phpmyadmin).*?" (?:400|401|403|404|444)ignoreregex = ^<HOST> - \S+ \[\] "GET \/healthz HTTP\/1\.[01]" 200
Developing a Filter for Custom Application JSON Logs
Cloud-native applications frequently output structured JSON logs.
Suppose your internal identity microservice records authentication failures as follows:
Never restart the Fail2Ban daemon without testing newly authored filters against real log data.
The fail2ban-regex utility executes dry-run evaluations against static files or single log lines:
# Test a custom filter against a log filefail2ban-regex /var/log/nginx/access.log /etc/fail2ban/filter.d/nginx-botsearch.local# Test a single log line directly from the terminalfail2ban-regex '198.51.100.89 - - [14/Oct/2026:14:32:01 +0000] "GET /.env HTTP/1.1" 404 162 "-" "curl/8.1.2"' \ '/etc/fail2ban/filter.d/nginx-botsearch.local'
Evaluating the terminal output verifies match accuracy and rule performance:
5. Kernel Packet Filtering: Migrating from iptables to nftables and ipset
The default action in legacy Fail2Ban setups invokes iptables to append individual DROP rules into a custom chain.
In enterprise environments with thousands of concurrent bans, this approach introduces severe performance bottlenecks.
The Problem with Linear iptables Chains
Legacy iptables evaluates rules sequentially.
If 5,000 IP addresses are banned, the Linux kernel must perform up to 5,000 string and pointer comparisons for every single inbound packet traversing the network stack.
This linear $O(N)$ computational complexity causes packet processing latency, spikes CPU hardware interrupts, and can degrade throughput under active volumetric load.
+----------------------------------------------------------------------------------------------------+| LINEAR IPTABLES CHAIN VS. CONSTANT-TIME NFTABLES SETS || || LEGACY IPTABLES (Linear Search - O(N)): || Inbound Packet ──> Rule 1 (IP 1?) ──> Rule 2 (IP 2?) ──> ... ──> Rule 5000 (Match?) ──> DROP || [ Latency increases with every additional banned IP; high kernel CPU load under attack ] || || MODERN NFTABLES / IPSET (Hash Map Lookup - O(1)): || Inbound Packet ──> Hash Table Lookup [ f2b-sshd set ] ──> Match Found! ───────────────> DROP || [ Constant sub-microsecond lookup time regardless of whether 10 or 100,000 IPs are banned ] |+----------------------------------------------------------------------------------------------------+
Implementing nftables Multiport Actions
Modern Linux distributions feature nftables as the modern replacement for iptables.
nftables provides native, kernel-level hash sets that execute lookups in constant $O(1)$ time.
To enforce nftables, verify the nftables userspace utility is installed:
# Verify nftables installation on Debian/Ubuntusudo apt-get update && sudo apt-get install -y nftables# Enable and start the nftables servicesudo systemctl enable nftablessudo systemctl start nftables
Update /etc/fail2ban/jail.local to enforce native nftables actions globally:
When Fail2Ban initializes with nftables-multiport, it establishes a dedicated table (f2b-table) and populates named sets.
Inspect active kernel sets using the native nft CLI:
# List Fail2Ban tables and active banned IP sets in nftablessudo nft list table inet f2b-table
table inet f2b-table { set addr-set-sshd { type ipv4_addr elements = { 198.51.100.23, 203.0.113.88, 192.0.2.14 } } chain f2b-sshd { type filter hook input priority filter - 1; policy accept; tcp dport 22 ip saddr @addr-set-sshd reject with icmp port-unreachable }}
By leveraging @addr-set-sshd, the Linux kernel drops or rejects malicious packets instantaneously, preserving full wire-speed routing capabilities.
6. Daily Operations, Telemetry, and SIEM Integration
Production engineering teams require operational runbooks for monitoring, manual intervention, and security metrics collection.
Essential CLI Administration Commands
Fail2Ban is administered through fail2ban-client:
# Check the operational status of the server and list active jailssudo fail2ban-client status# Output detailed telemetry for a specific jail (sshd)sudo fail2ban-client status sshd# Manually ban an abusive IP address immediatelysudo fail2ban-client set sshd banip 198.51.100.120# Manually unban an IP (e.g., in the event of an accidental admin lockout)sudo fail2ban-client set sshd unbanip 198.51.100.120# Unban an IP across ALL configured jails simultaneouslysudo fail2ban-client unban 198.51.100.120# Reload configuration without dropping existing active banssudo fail2ban-client reload
Inspecting the output of fail2ban-client status sshd provides instant visibility into defensive operations:
Status for the jail: sshd|- Filter| |- Currently failed: 3| |- Total failed: 412| `- File list: systemd`- Actions |- Currently banned: 14 |- Total banned: 89 `- Banned IP list: 198.51.100.14 203.0.113.72 192.0.2.99 ...
Exporting Metrics to Prometheus and Grafana
To achieve observability across distributed server fleets, deploy fail2ban-exporter to surface operational metrics to Prometheus.
The exporter queries fail2ban-server via its Unix domain socket (/var/run/fail2ban/fail2ban.sock) and exposes standard metrics on port 9191:
# HELP fail2ban_up Shows if fail2ban is up and running (1 = up, 0 = down).# TYPE fail2ban_up gaugefail2ban_up 1# HELP fail2ban_failed_current Number of currently failed attempts per jail.# TYPE fail2ban_failed_current gaugefail2ban_failed_current{jail="sshd"} 3fail2ban_failed_current{jail="nginx-botsearch"} 1# HELP fail2ban_banned_current Number of currently banned IPs per jail.# TYPE fail2ban_banned_current gaugefail2ban_banned_current{jail="sshd"} 14fail2ban_banned_current{jail="recidive"} 4# HELP fail2ban_banned_total Total number of banned IPs since startup.# TYPE fail2ban_banned_total counterfail2ban_banned_total{jail="sshd"} 89
With these metrics ingested into Grafana, security operations teams can configure alerts for unexpected ban spikes, detect coordinated brute-force campaigns, and track geographic threat distributions.
7. Actionable Governance, Compliance, and Implementation Checklist
Intrusion prevention is not merely an operational convenience; it is a foundational compliance mandate across modern cybersecurity frameworks.
Framework Alignment Matrix
Standard / Framework
Requirement / Control
Fail2Ban Technical Implementation
ISO/IEC 27001:2022
A.8.7 (Protection against malware)
Blocks automated exploit injection scripts and bot-driven web reconnaissance.
ISO/IEC 27001:2022
A.8.16 (Monitoring activities)
Continuous real-time audit log parsing with automated event correlation.
ISO/IEC 27001:2022
A.8.20 (Network security)
Dynamic netfilter access control list updating at the host network layer.
NIST SP 800-53 Rev. 5
AC-7 (Unsuccessful Logon Attempts)
Automatically enforces temporary or progressive lockouts after $N$ failed authentications.
NIST SP 800-53 Rev. 5
SI-4 (System Monitoring)
Ingests OS authentication telemetry to identify anomalous intrusion patterns.
PCI DSS v4.0
Requirement 8.3.4
Limits repeated access attempts by locking out user accounts or source network addresses.
PCI DSS v4.0
Requirement 10.4.1
Provides auditable ban and unban records within central logging facilities.
Production Implementation and Hardening Checklist
Follow this systematic checklist when onboarding new servers into production:
Package Verification: Install Fail2Ban and verify the daemon initializes as a managed systemd unit.
Configuration Isolation: Create /etc/fail2ban/jail.local and ensure upstream jail.conf remains pristine.
Infrastructure Whitelisting: Configure ignoreip with all corporate jump hosts, monitoring probes, and local CIDRs.
Netfilter Upgrade: Configure banaction = nftables-multiport to replace legacy linear iptables chains.
Backend Selection: Set backend = systemd for services logging to journald, and pyinotify for static text logs.
Progressive Ban Durations: Activate bantime.increment = true to penalize persistent botnets with exponential backoff.
Recidive Enforcement: Activate the recidive jail with a 30-day quarantine for multi-jail repeat offenders.
Filter Validation: Execute fail2ban-regex against real production logs to ensure zero false negatives and zero catastrophic backtracking.
Log Rotation Resilience: Verify that logrotate directives issue fail2ban-client flushlogs post-rotation to rebind active file descriptors.
Strategic Summary
Host-based intrusion prevention with Fail2Ban remains an indispensable security control in defense-in-depth architecture.
While perimeter firewalls and cloud edge providers protect external entry points, Fail2Ban provides granular, automated, host-level enforcement that shuts down opportunistic reconnaissance and brute-force attacks at the kernel level.
By replacing legacy iptables invocations with modern nftables sets, implementing progressive exponential bans, deploying the recidive jail, and establishing custom regex filters, security teams transform passive log trails into proactive defense barriers.
Ensure your deployments enforce strict configuration hierarchy, maintain verified administrative whitelists, and export telemetry to centralized SIEM pipelines to maintain an authoritative, resilient security posture across your fleet.
 Cybersecurity