Securing VoIP Infrastructure: Blue Team Tactics Against SIP Exploits
A deep dive into defending VoIP infrastructure against SIP-based exploits, with actionable Blue Team strategies and technical detection techniques.
A comprehensive article on Voice over Internet Protocol (VoIP), detailing its core technologies, the key protocols that enable it, and the significant security threats it faces.
Understand Linux privileges and explore common privilege escalation techniques used in red team operations, with practical examples and code snippets.
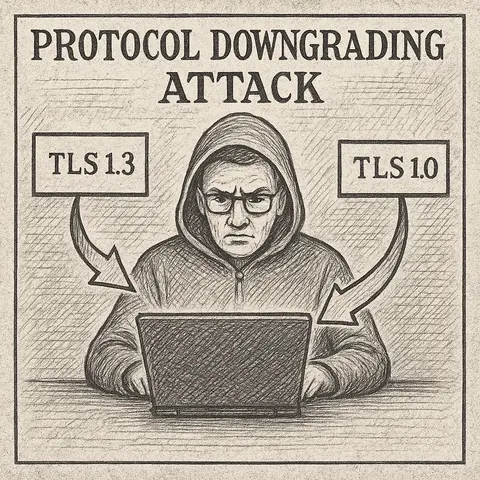
A deep dive into protocol downgrading attacks, how they work, real-world examples, and code demonstrations to help security operators understand and detect them.
A deep dive into Linux log investigation techniques, tools used by cybersecurity professionals, real-world scenarios, and practical code examples.
A deep dive into OpenSSL, its capabilities, practical uses, and why it's more than just a certificate generator.
Learn how Linux processes work, and how security defenders (blue team) can use process monitoring tools to detect intrusions, anomalies, and breaches.
A comprehensive guide for blue team analysts to monitor, investigate, and hunt malicious activity in Windows processes using built-in tools, PowerShell, and Sysmon.
A comprehensive guide on how red teams and penetration testers can leverage the `find` command for reconnaissance, privilege escalation, and post-exploitation activities. Includes practical code samples for reference.
An in-depth look at the 'Echo Chamber' exploit, a novel social engineering technique that leverages AI and personalized content algorithms to manipulate individuals and organizations.